The design of industrial machines requires skills in mechanics, automation, and risk analysis. With the new European regulation on machine safety applicable from January 20, 2027, regulatory requirements now weigh on every phase of the project, from the preliminary study to dismantling. Which workstations concentrate the most technical constraints, and where are the gaps between a traditional approach and an approach compliant with the upcoming regulatory framework?
Comparison of Design Phases: Traditional Approach and Regulatory Framework 2027
Most design offices structure their projects into four to six successive phases. The new European regulation does not eliminate any of these phases but modifies their scope and the expected deliverables.
| Phase | Traditional Approach | Regulation 2027 Requirements |
|---|---|---|
| Needs Analysis | Functional specifications, production constraints | Mandatory integration of hazard analysis from this phase |
| Mechanical Design (CAD) | 3D modeling, material selection (steel, alloys) | Technical documentation tracing each safety-related choice |
| Automation and Software Design | CNC axis programming, operator interfaces | Industrial cybersecurity aspect for connected machines |
| Prototyping and Testing | Functional tests, machining and precision adjustments | Formal validation of compliance before market release |
| In-Service Modification | Managed by the end user, without strict framework | Any substantial modification imposes the obligations of a manufacturer |
The most notable gap concerns the in-service modification phase. Until now, an integrator or end user could adapt a machine without bearing the regulatory responsibility of the original manufacturer. Any substantial modification now triggers the same compliance obligations as new manufacturing.
To better understand the design stages of industrial machines, it is essential to assess how this change redistributes responsibilities among the client, design office, and operator.
Cybersecurity of Connected Machines: An Underestimated Design Aspect
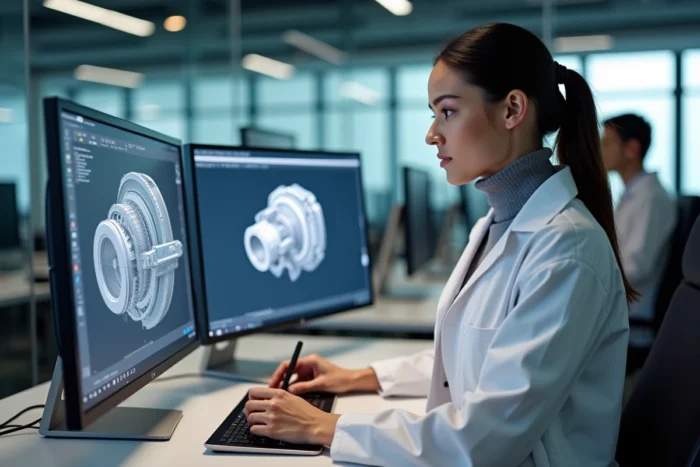
Recent CNC machines come equipped with remote connections for predictive maintenance, software updates, or multi-axis control. Regulation 2027 transforms this connectivity into a design obligation: no cybersecurity vulnerability should create a dangerous situation for operators or the installation.
In practical terms, the design office must integrate industrial cybersecurity at the same level as mechanical sizing or the choice of machining tools. This involves several additional deliverables:
- A mapping of remote access and communication protocols used by the machine
- A risk analysis specific to software vulnerabilities, distinct from the traditional mechanical risk analysis
- A secure firmware update plan, documented in the technical file
- Intrusion or network robustness tests before the final validation of the prototype
This aspect significantly extends the automation design phase. Teams designing multi-axis CNC machines or automated assembly lines must anticipate this additional cost from the specifications stage.
Traceability of Design Choices: Materials, Machining, and Documentation
The mechanical design of an industrial machine relies on trade-offs between materials (steel, aluminum, technical plastics), machining processes (milling, turning, digital cutting), and dimensional precision constraints. Each trade-off directly impacts manufacturing costs and the lifespan of the parts.
The upcoming regulatory framework requires that every safety-related choice be traced in the technical documentation. A design office that opts for a specific grade of steel for a machine frame must justify this choice based on the hazard analysis, and not just on mechanical strength.
Where Traceability Changes Daily Practice
In traditional design, the choice of a material or CNC machining process is subject to an internal calculation note. With the new regulation, this note becomes a regulatory deliverable that can be consulted by market surveillance authorities.
Complex parts machined on multi-axis machines pose a particular challenge. Their geometry sometimes makes complete dimensional inspection after manufacturing difficult. On-machine inspection during machining becomes an asset to document the compliance of each critical part.
Extended Hazard Analysis Until Dismantling: What This Changes Upstream
Traditionally, risk analysis covers the normal use phase and predictable maintenance situations. Regulation 2027 extends this analysis to the entire lifecycle, including the dismantling of the machine.
This extension has direct consequences on the design phase:
- Assemblies must be designed for safe disassembly (access to lockout points, absence of residual stresses in springs or cylinders)
- Hazardous materials (certain technical plastics, coatings, cutting fluids) must be identified, and their disposal procedures documented
- The technical file must include dismantling instructions, not just assembly and usage instructions
For a designer used to delivering a functional machine, considering dismantling from the initial design represents a change in mindset. Current CAD tools do not offer a dedicated module for this analysis, forcing teams to develop their own evaluation grids.
Expanded Responsibility: Integrators and End Users Under the Same Regime
One of the most structuring points of the new framework concerns the broadening of the notion of manufacturer. An end user who modifies a machine (adding an axis, changing an automated cutting tool, reprogramming a safety PLC) can be requalified as a manufacturer if the modification is deemed substantial.
This requalification entails the obligation to redo a complete compliance analysis, to create a technical file, and to apply a new marking. Companies that operate fleets of older machines and regularly upgrade them are directly affected.
The boundary between routine maintenance and substantial modification remains a point of interpretation. Initial feedback from control bodies after the regulation comes into force will help stabilize the criteria. Until then, systematically documenting any technical intervention on a machine in service is the most reliable precaution.